

As AI agents gain access to enterprise systems and data, security teams are having to secure not just infrastructure, but the identities, permissions and decisions through which machines act.
The enterprise security perimeter is no longer confined to servers, applications and networks. As AI agents gain access to business systems, data and workflows, the more difficult question for security teams is increasingly who—or what—is authorised to act, and under whose authority.
AI systems can inherit permissions, API tokens and service-level access assigned to human employees or existing workflows. Unlike employees, however, machines may continue operating without the same offboarding or entitlement reviews.
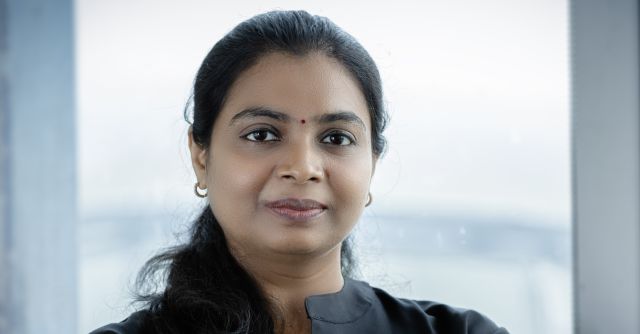
This creates what Subhalakshmi Ganapathy, Chief IT Security Evangelist at ManageEngine, calls an “unmonitored persistence pathway”.
“AI-first transformation is not failing on intelligence; it is failing on identity discipline,” Ganapathy said.
The problem extends beyond access management. As enterprises deploy AI across increasingly sensitive processes, the security stack itself is expanding to include prompts, models, training data, APIs, orchestration chains and tool-call permissions.
That makes the traditional perimeter-centric approach inadequate, she said. Security teams must instead focus on whether AI-driven decision pathways are constrained, observable and reversible.
This is particularly relevant when AI systems interact with sensitive enterprise information. Security controls need to establish not only whether data is protected from theft, but whether it is being used for the purpose for which it was collected. Ganapathy points to purpose limitation, retention and deletion controls as important safeguards, alongside model inventories, API governance and auditable checkpoints.
The rise of non-human identities (NHIs) makes the challenge harder. Service accounts, connectors, tokens and agent credentials increasingly link data ingestion and inference to downstream actions. If these identities are over-privileged or poorly monitored, attackers may not need to compromise an AI model at all. They can exploit trusted credentials and pathways to access information or trigger legitimate-looking operations.
That shifts the security question from “Is the model secure?” to “What can this system do, with which credentials, and what happens when it makes a wrong decision?”
Ganapathy argues that accountability therefore needs to be embedded into the architecture rather than added through policy documents. One approach is decision tiering: low-impact actions can be automated, medium-impact actions subjected to policy checks, and high-impact decisions routed to human approval.
Policy-as-code guardrails, traceable decision logs, immutable audit records, emergency kill switches and fallback workflows can provide additional control. “Autonomy without accountability is acceleration without control,” she said.
For CIOs and CISOs, the challenge is to introduce these controls without turning security into a barrier to AI adoption. Ganapathy recommends a staged maturity approach rather than rapid deployment, with phased onboarding, risk-classification gates, common policy baselines and clearly defined ownership.
Security operations will also need broader telemetry. Identity events, endpoint activity, cloud environments, APIs and AI-runtime signals need to be correlated so that teams can identify unusual behaviour and privilege escalation earlier. AI can help with detection and prioritisation, but humans should retain authority over high-impact containment decisions.
“The AI security race will not be won by who deploys more AI, but by who operationalises better intelligence,” Ganapathy said.
For enterprises scaling autonomous systems, the priorities are consequently broader than model security: govern non-human identities, protect data through its lifecycle, and build resilience into autonomous workflows through red-teaming, abuse simulations, fail-safe mechanisms and incident-response exercises.
As machines acquire greater agency inside the enterprise, the security perimeter is becoming less about where systems reside and more about what they are allowed to do.

Leave a Reply