
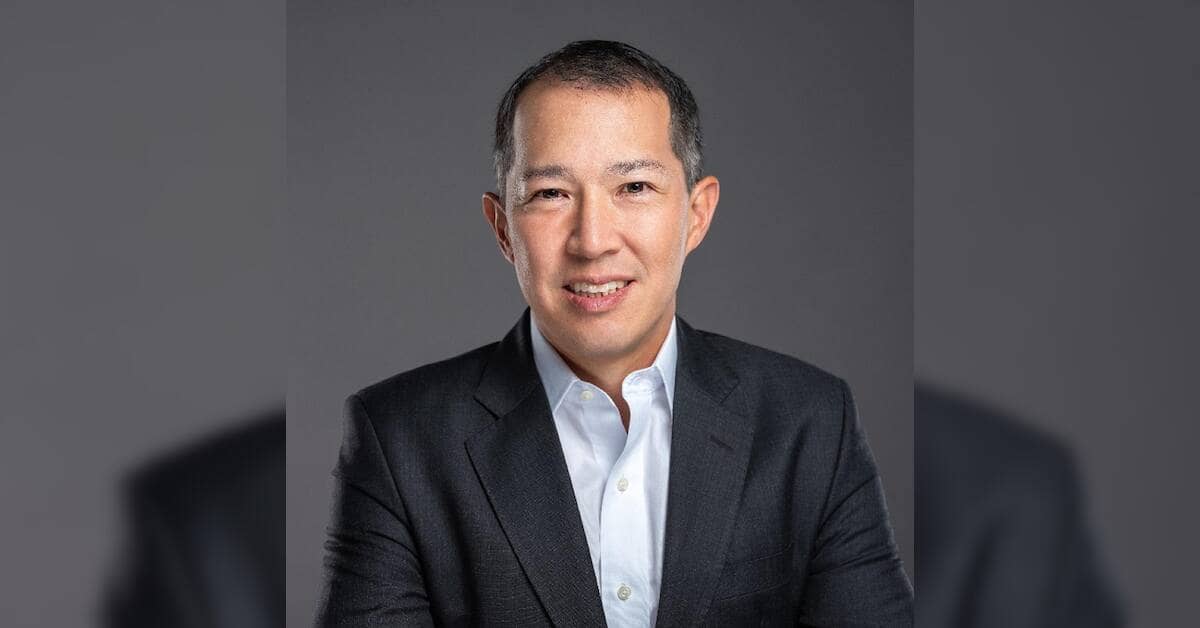
Mike Yeh, vice-president and deputy general counsel of customer security and trust at Microsoft, believes that enterprises must give AI agents the least amount of privilege and access to their networks to contain them and prevent overreach.
“When you look at how consumers are using agents today…they are giving them access to their email, bank accounts. You can see why that will create problems in the near term. As we get smarter about that, we have to change the mentality. The default is the least amount of privileges for the agent to do its task,” Yeh told Business Standard in an exclusive interaction in New Delhi.
There should also be more transparency from companies developing frontier AI models about the capabilities of the AI agents they are releasing to users, so that “there is a better understanding of what the consequences could be,” Yeh said.
Speaking about the 2026 Microsoft Digital Defense Report, Yeh said that while most cyberattacks still exploit old vulnerabilities, going forward, everything would have to be seen through the lens of how AI has affected it.
“We have a very small window right now to get the basics right. For example, vulnerabilities from the year 2020 that were exploited this year should have been patched. This is where the industry needs to do its homework before people start using AI in a way that really compresses the attack cycle timeline for us,” he said.
To give enterprises and customers more options and control over their digital networks, Microsoft has also introduced new control options for Azure users, Yeh said.
Earlier on Tuesday, Microsoft’s chief executive officer Satya Nadella announced a host of new initiatives from the company on the expansion of sovereign cloud capabilities, including giving Azure users a unified way to assess their sovereignty posture, identify gaps in their existing Azure capabilities, apply the necessary guardrails according to the rules of the country of operation, and retain evidence of qualifying Microsoft operator access.
Speaking about the new initiatives announced by Nadella on Tuesday, Alistair Speirs, general manager at Microsoft Azure, said different countries now had varying definitions of sovereignty, so companies did not have a mandatory set list of standards they must meet.
“So we really think of sovereignty as a risk management exercise. And as a risk management exercise, it sits alongside other risks, including business continuity, natural disasters, and cybersecurity,” Speirs said during a select media roundtable.

Leave a Reply